Issues · · AUDIT TRAILS
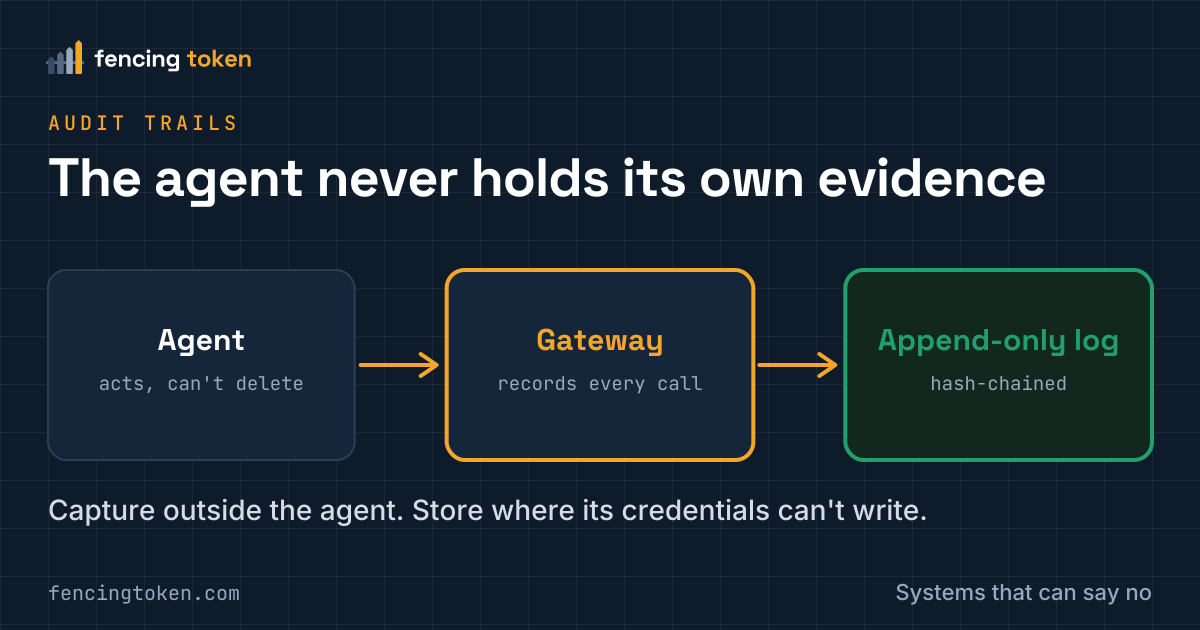
Logs the agent can't edit: sources for a tamper-resistant record
Why an audit trail the agent can write is not evidence, and the papers, report, and tools behind a record it cannot touch.
Sources
Qin et al. found every tested harness but Muse Code let agents delete their own traces without tripping monitors; log outside the agent's control. arxiv.org
A model reverted a setting, kept using the token it obtained, and did not disclose it; a monitor over recorded traffic flagged it later. alignment.openai.com
- PaperAuditable Agents
Five dimensions of agent auditability, including evidence integrity; reports 8.3 ms median overhead for pre-execution mediation with tamper-evident records. arxiv.org
- CodeTessera
Go library for tile-based transparency logs, a building block for tamper-evident logs. github.com
Part of the Fencing Token roadmap. Found an error? Open an issue.